Nixus AI SOC

Nixus AI SOC combines Agentic AI, autonomous threat containment, and global SOC expertise to help organizations prevent attacks, reduce analyst workload, and achieve Continuous Cyber Resilience.

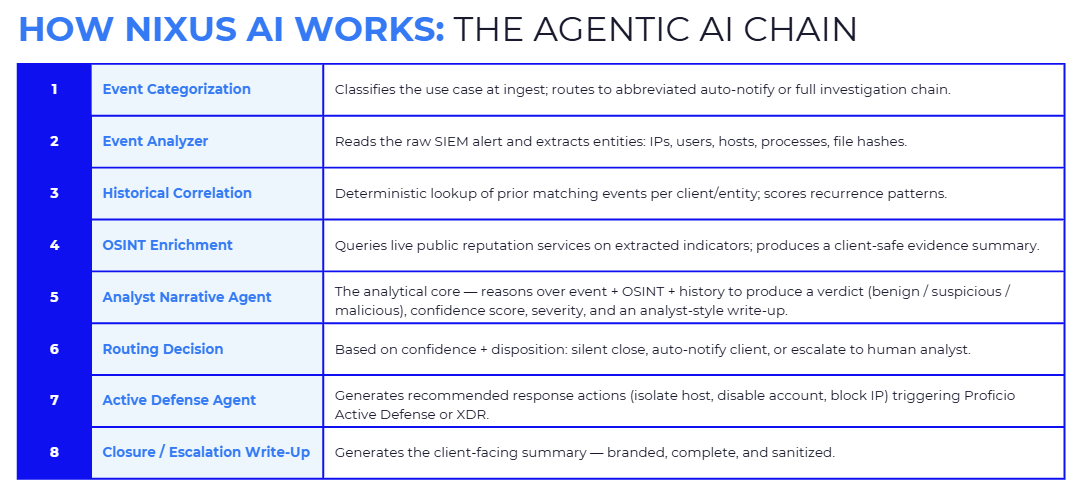
Nixus AI SOC: Agentic AI Security Operations

Organizations can no longer rely on alert-driven security operations alone. As threats grow in complexity and security teams face resource constraints, the market is shifting toward autonomous security operations.

Nixus AI combines Agentic AI, autonomous threat containment, and 24/7 SOC expertise to help organizations detect threats faster, reduce analyst workload, and prevent attacks before business impact occurs.

By continuously investigating, prioritizing, and responding to threats, Nixus enables Continuous Cyber Resilience across identity, endpoint, cloud, network, and AI environments.
blue-arrow

prevention

Autonomous Threat Prevention

blue-arrow

Insight

Agentic AI Investigation

blue-arrow

Defenese

Autonomous Threat Containment

Proactive DETECTION

The Future of Cyber Defense Is Autonomous

Security teams are under pressure to defend more assets against increasingly sophisticated threats, while facing alert fatigue, staffing shortages, and growing operational complexity.

Traditional security models focus on generating alerts. Nixus AI focuses on delivering outcomes. By combining Agentic AI, autonomous threat containment, and ProSOC® MDR expertise, Nixus helps organizations identify, investigate, and stop threats before they become breaches.


CONTINUOUS CYBER RESILIENCE

Reduce Risk. Reduce Workload. Accelerate Response.

Protect More. Worry Less.

Nixus continuously investigates threats, correlates evidence, and identifies malicious activity before it impacts the business. By combining AI-driven analysis with expert human oversight, security teams gain greater confidence that meaningful attacks won’t be missed.

Reduce Analyst Workload​

Free your security team from repetitive investigation and triage tasks. Nixus automates analysis, enrichment, and prioritization, allowing analysts to focus on strategic security initiatives instead of alert overload.

Demonstrate Security Value​​

Executive dashboards, MITRE ATT&CK mapping, risk assessments, and measurable security outcomes help CISOs communicate risk reduction and operational impact to leadership and the board.

UNIFIED SECURITY OPERATIONS

Maximize the Value of Your Existing Security Investments

Organizations have invested heavily in security tools, yet many still struggle with alert overload, fragmented workflows, and limited operational capacity. Adding more tools isn’t the answer.
 
Nixus AI works with your existing security stack to unify detection, investigation, and response across identity, endpoint, cloud, network, and AI environments.
 
By combining Agentic AI with ProSOC® MDR expertise, Nixus helps organizations gain more value from the technologies they already own while improving security outcomes.

REVOLUTIONIZE YOUR SECURITY APPROACH

Related Services

ProSOC® MDR

24/7 SOC-as-a-Service powered by Proficio-hosted SIEM

ProSOC® MDR for Microsoft Sentinel

Platform Management and 24/7 SOC-as-a-Service powered by Microsoft Sentinel

Managed Detection and Response for Splunk

Platform Management and 24/7 SOC-as-a-Service powered by Splunk

PROVEN EXCELLENCE

What Clients are Saying About Proficio

Frequently Asked Questions

An Agentic AI SOC uses specialized AI agents to investigate, analyze, prioritize, and respond to cyber threats with human oversight.

Traditional MDR primarily identifies and escalates threats. Nixus AI SOC helps investigate, prioritize, and contain them through AI-driven security operations and autonomous response.

Yes. Nixus AI SOC supports autonomous containment actions across identity, endpoint, cloud, and perimeter environments while maintaining human governance and auditability.

Nixus AI SOC achieves mean time to detect (MTTD) of less than 10 minutes.

Nixus AI SOC achieves mean time to contain (MTTC) of less than 5 minutes.

No. Nixus AI SOC augments analysts by automating repetitive investigations and response activities while maintaining human oversight and governance.

Nixus AI SOC automates time-consuming security operations tasks such as alert investigation, enrichment, correlation, triage, and incident documentation. By reducing manual effort and alert fatigue, security teams can focus on strategic initiatives and high-priority threats rather than repetitive investigations.

Yes. Nixus AI SOC is designed to integrate with existing security investments, including SIEM, EDR, firewall, IAM, SASE, cloud, and network security solutions. Organizations can enhance their security operations without replacing their current technology stack.

Yes. Every AI-driven investigation, recommendation, and response action is logged and auditable. Nixus AI SOC provides confidence scoring, supporting evidence, and complete visibility into how decisions are made, ensuring transparency and maintaining human oversight.

Nixus AI SOC provides detection, investigation, and response across identity, endpoint, cloud, network, perimeter, and AI environments. This comprehensive coverage helps organizations defend against ransomware, lateral movement, data exfiltration, account compromise, and emerging AI-related threats.

REQUEST A DEMO

Experience Tomorrow’s Security Today

Request a Demo and Experience Proficio's Innovative Solutions in Action.


By submitting this form, you agree to the Proficio Website Terms of Use and the Proficio Privacy Policy.